

 Global
 Belgium
 Denmark
 Finland
 Germany
 Malaysia
 Netherlands
 Norway
 Poland
 Sweden
 UK
WHY IT MATTERS
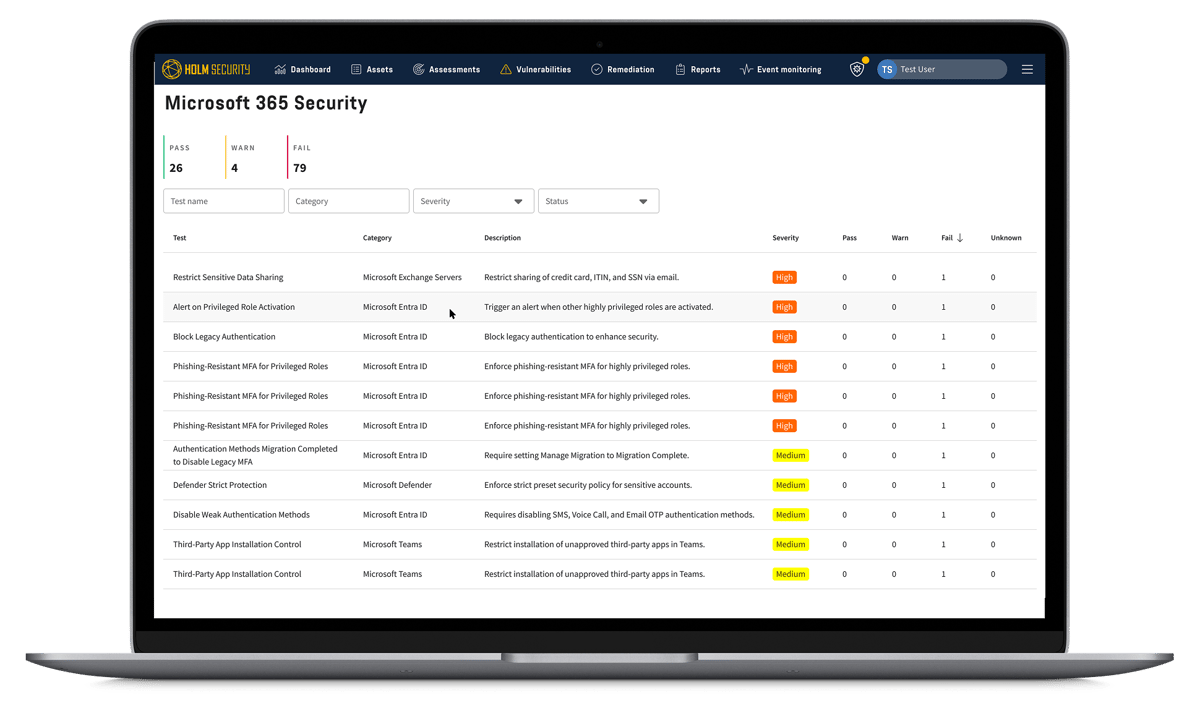
Reduce your Microsoft 365 attack surface
- Harden your Microsoft 365 tenant before cybercriminals exploit default settings built for ease, not security.
- Replace manual reviews and one-off audits with continuous, scheduled assessments inside the platform you already use.
- Build a systematic, repeatable cybersecurity approach as required by NIS2 and DORA.
- Prove your Microsoft 365 baseline holds over time, with severity-based prioritization, remediation guidance, and reporting built in.
- Get an independent view alongside Microsoft Secure Score, measured against the CISA SCuBA federal baseline instead of vendor-only recommendations.
"Holm Security has become an integral part of our cyber security strategy, helping us protect client data, meet compliance requirements, and maintain operational resilience."
"Since implementing Holm Security's Next-Gen Vulnerability Management Platform, we continuously monitor vulnerabilities and know where we are vulnerable."
"The data and visibility we've received from Holm Security's platform have allowed us to set up regular scanning of our OT environment, reduce our risk score, and remove vulnerabilities - from software and hardware alike. I'm very happy with the progress we've made, and our CSM is always on hand when needed."
"Holm Security's Customer Success and Support & Delivery teams have been instrumental in helping us interpret and act on the extensive data gathered from our IT environment scans. Their guidance has enabled us to transform raw scan results into meaningful insights, giving us a clear, comprehensive overview of our infrastructure. We can now effectively prioritize our assets and vulnerabilities based on business relevance, significantly improving our ability to manage risk and maintain a stronger security posture."
"With Holm Security, we identify vulnerabilities as they emerge in our environment and gain deep insight into their severity, exploitability, and business impact. The platform delivers clear and actionable remediation guidance, enabling us to prioritize risks correctly and address them efficiently."
"Both the platform and the support have worked well from the start. From network and web application scanning to Customer Success, Holm Security delivers what we need."